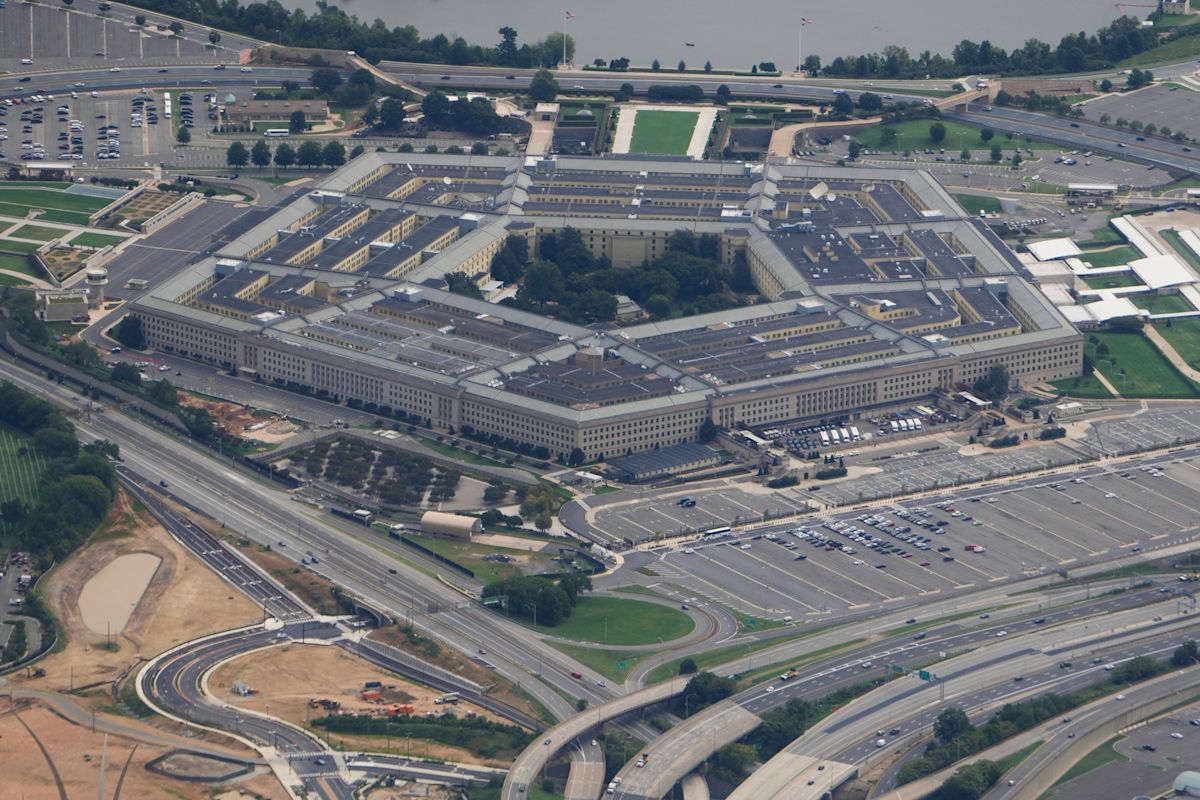
A breach of the Pentagon’s extensive personnel database exposed sensitive information belonging to a massive swath of military personnel, including Social Security numbers and details about the jobs they held, according to a US defense official. The violation affected 2.76 million living people and another 294,000 dead, the official said. The scope and sensitivity of the information exposed could raise national security concerns, particularly because the files included details about jobs performed by military and civilian personnel. “A Defense Manpower Data Center (DMDC) information system experienced unauthorized access to personally identifiable information by a small number of unauthorized users between October 2025 and July 2026. Upon discovery, DMDC immediately fixed the vulnerability,” the official said. Julia Demaree Nikhinson/AP – PHOTO: The Pentagon as seen from Air Force One, September 2021 December 26, 2026, in Washington, DC The Defense Manpower Data Center serves as one of the Pentagon’s main repositories for personnel records, containing information on active duty and reserve troops, civilian employees, contractors, retirees, veterans and military family members. FBI investigating possible cyber breach of its job application website: Sources The agency maintains more than 60 million personnel records. Military Times first reported the breach last week. The unauthorized access extended from October 2025 to July, when DMDC discovered the vulnerability and patched the affected system, according to the defense official, adding that there is still no evidence that any of the exposed data was misused. Defense officials said they have found no evidence so far that the exposed information was misused and are offering identity protection and credit monitoring resources. News of the Pentagon breach comes as the FBI sent a notice to employees on Friday outlining its response to a breach of its FBIJobs.gov job portal. A threat actor said he would release data including FBI employees’ names, addresses, personal and work contact information, Social Security numbers, date of birth and emergency contact information, sources told ABC News, and the bureau is operating as if every FBI employee’s personal information was compromised. But in a statement to the New York Times and 404 Media on Monday, the hacking group shinyhunters said it will not release the data as it had previously said it would. “From the beginning of this event we have unequivocally and assiduously emphasized that this is NOT extortion, it is NOT ransom, it is NOT financially motivated,” the statement said. “This was all a marketing campaign to protect our business and actively combat misinformation. If we were making this statement normally, such attention to our words and intentions would never have been so widespread.” ABC News has not independently verified the group’s claims. Employees who were affected also began to be notified, and the FBI said the affected system, FBIJobs.gov, was unclassified. The FBI also issued a warning to those who might be affected, advising them to maintain situational awareness and not to answer suspicious calls. There will also be internal briefings for employees who have been affected. seen affected. It also says, according to the warning described to ABC News, that employees should not talk to the media and if the media is “invading,” employees should call 911.