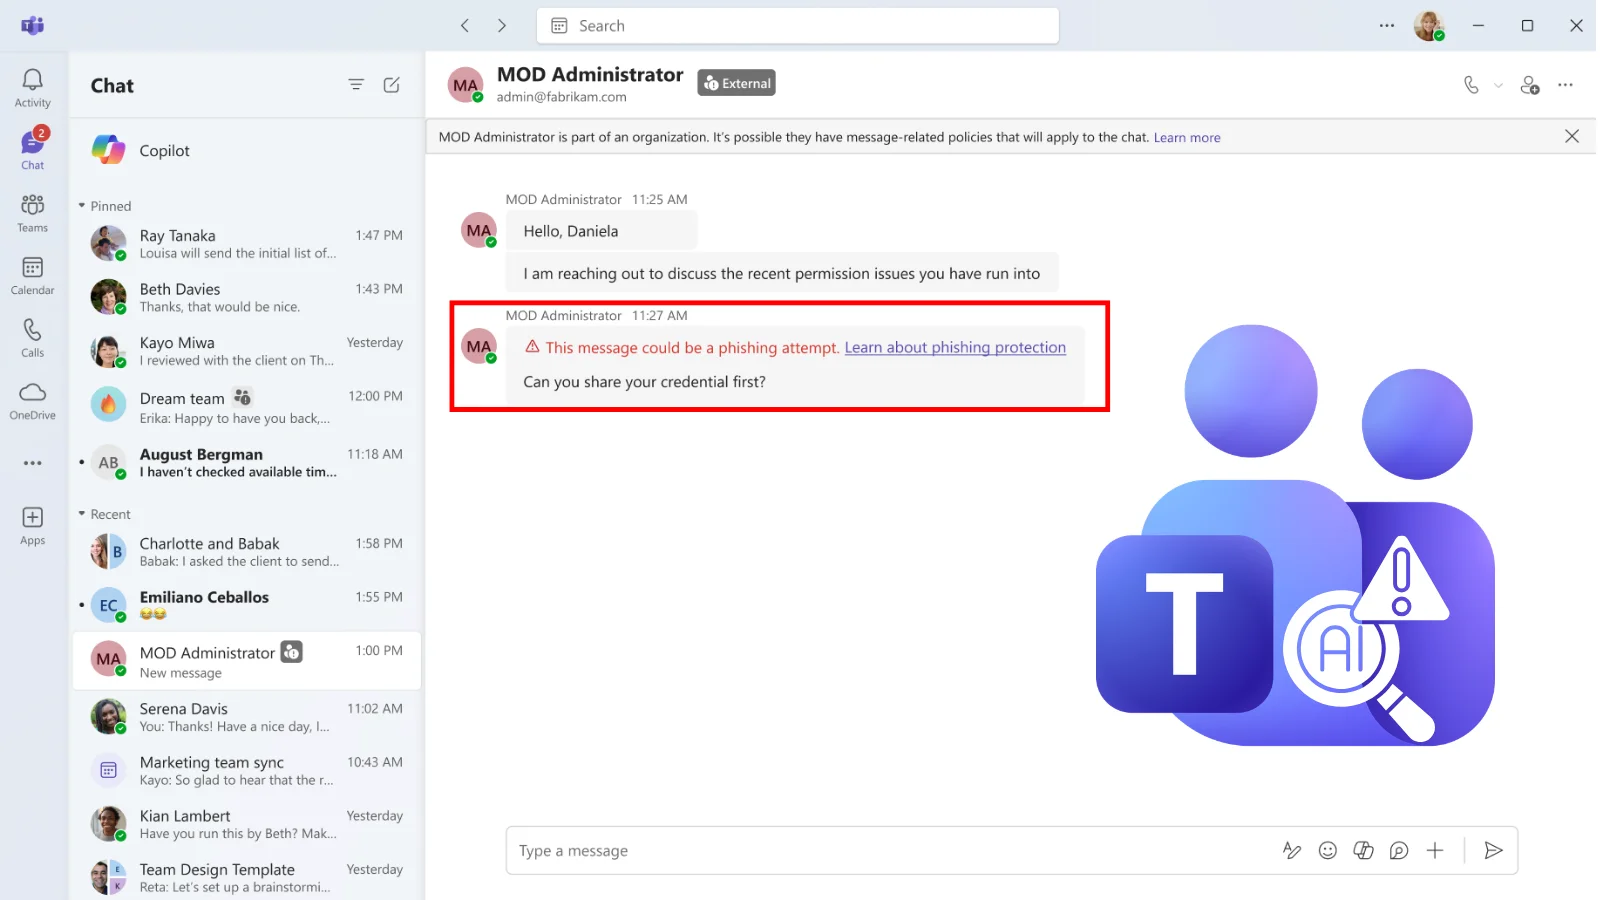
Microsoft is preparing to add AI phishing detection to Microsoft Teams, using conversation context to detect scams that may not contain harmful links or attachments. The feature will primarily focus on early conversations with external contacts, where attackers can impersonate trusted support staff and ask employees to share sensitive information. Microsoft detailed the change in Message Center notice MC1519866, published on October 21, 2026. The specific release is scheduled to begin in early November and end in mid-November. Global general availability is expected to begin in early December and end in mid-December, rather than reaching all customers in November. How conversation context helps detect phishing Traditional warning signs, such as suspicious links and infected files, are not always present in social engineering attacks. Instead, a message can build trust, report an urgent account issue, and persuade someone to reveal a password or approve remote access. Microsoft says the new capability will analyze conversation context to identify phishing, spoofing, social engineering, and deceptive intent. Their support guide outlines coverage for one-on-one and group chats involving new external contacts on mobile, desktop, and web. Roadmap entry 575288 lists Android, iOS, Mac, desktop, and web support for the global standard cloud. The warning example accompanying the ad shows an external account called “MOD Administrator” discussing permissions issues before asking, “Can you share your credential first?” Teams displays a notice saying the message could be a phishing attempt. The example illustrates why the meaning of a conversation can matter even without a dangerous URL. Source: Microsoft This addresses a familiar attack pattern. Cybersecurity News previously reported on attackers posing as IT help desk staff through Teams, using compelling support requests to push users toward malware or remote access. Separate reports described fake support operators abusing Quick Assist after contacting employees through external Teams accounts. Microsoft says the detection can initially run silently while checking quality. Visible warnings may appear after that validation, so users should not expect every suspicious message to trigger an immediate banner upon launch. For most users, protection focuses on first contact external chats. Teams mobile users in China can also receive protection for conversations within their own organization, reflecting fraud patterns seen in that region. This is a specific extension, not a promise of universal internal chat scanning. Microsoft says the capability is for security purposes only. It is not intended for advertising, employee tracking, productivity analysis, or conversation summaries. The detection system does not retain the content of client messages for model training or other secondary uses. That statement should not be read as a change to all existing Teams retention policies. What organizations should do No new administrator configuration is required to enable protection. However, Microsoft recommends reviewing the guidelines for unknown external contacts and encouraging users to report suspicious activity or incorrect detections. When a warning appears, employees should verify the identity and email address of the sender through a trusted channel. Microsoft recommends blocking and reporting confirmed phishing, while erroneous warnings can be considered not concerning. Users should never share passwords, verification codes, financial details, or sensitive information through an unexpected support conversation. The update adds another layer of warning, but staff still need to independently verify unexpected support requests and report suspicious contacts, rather than treating the absence of a banner as proof of security. Update defenses against new malware as soon as it appears. Integrate TI Feeds with 16K SOC data.