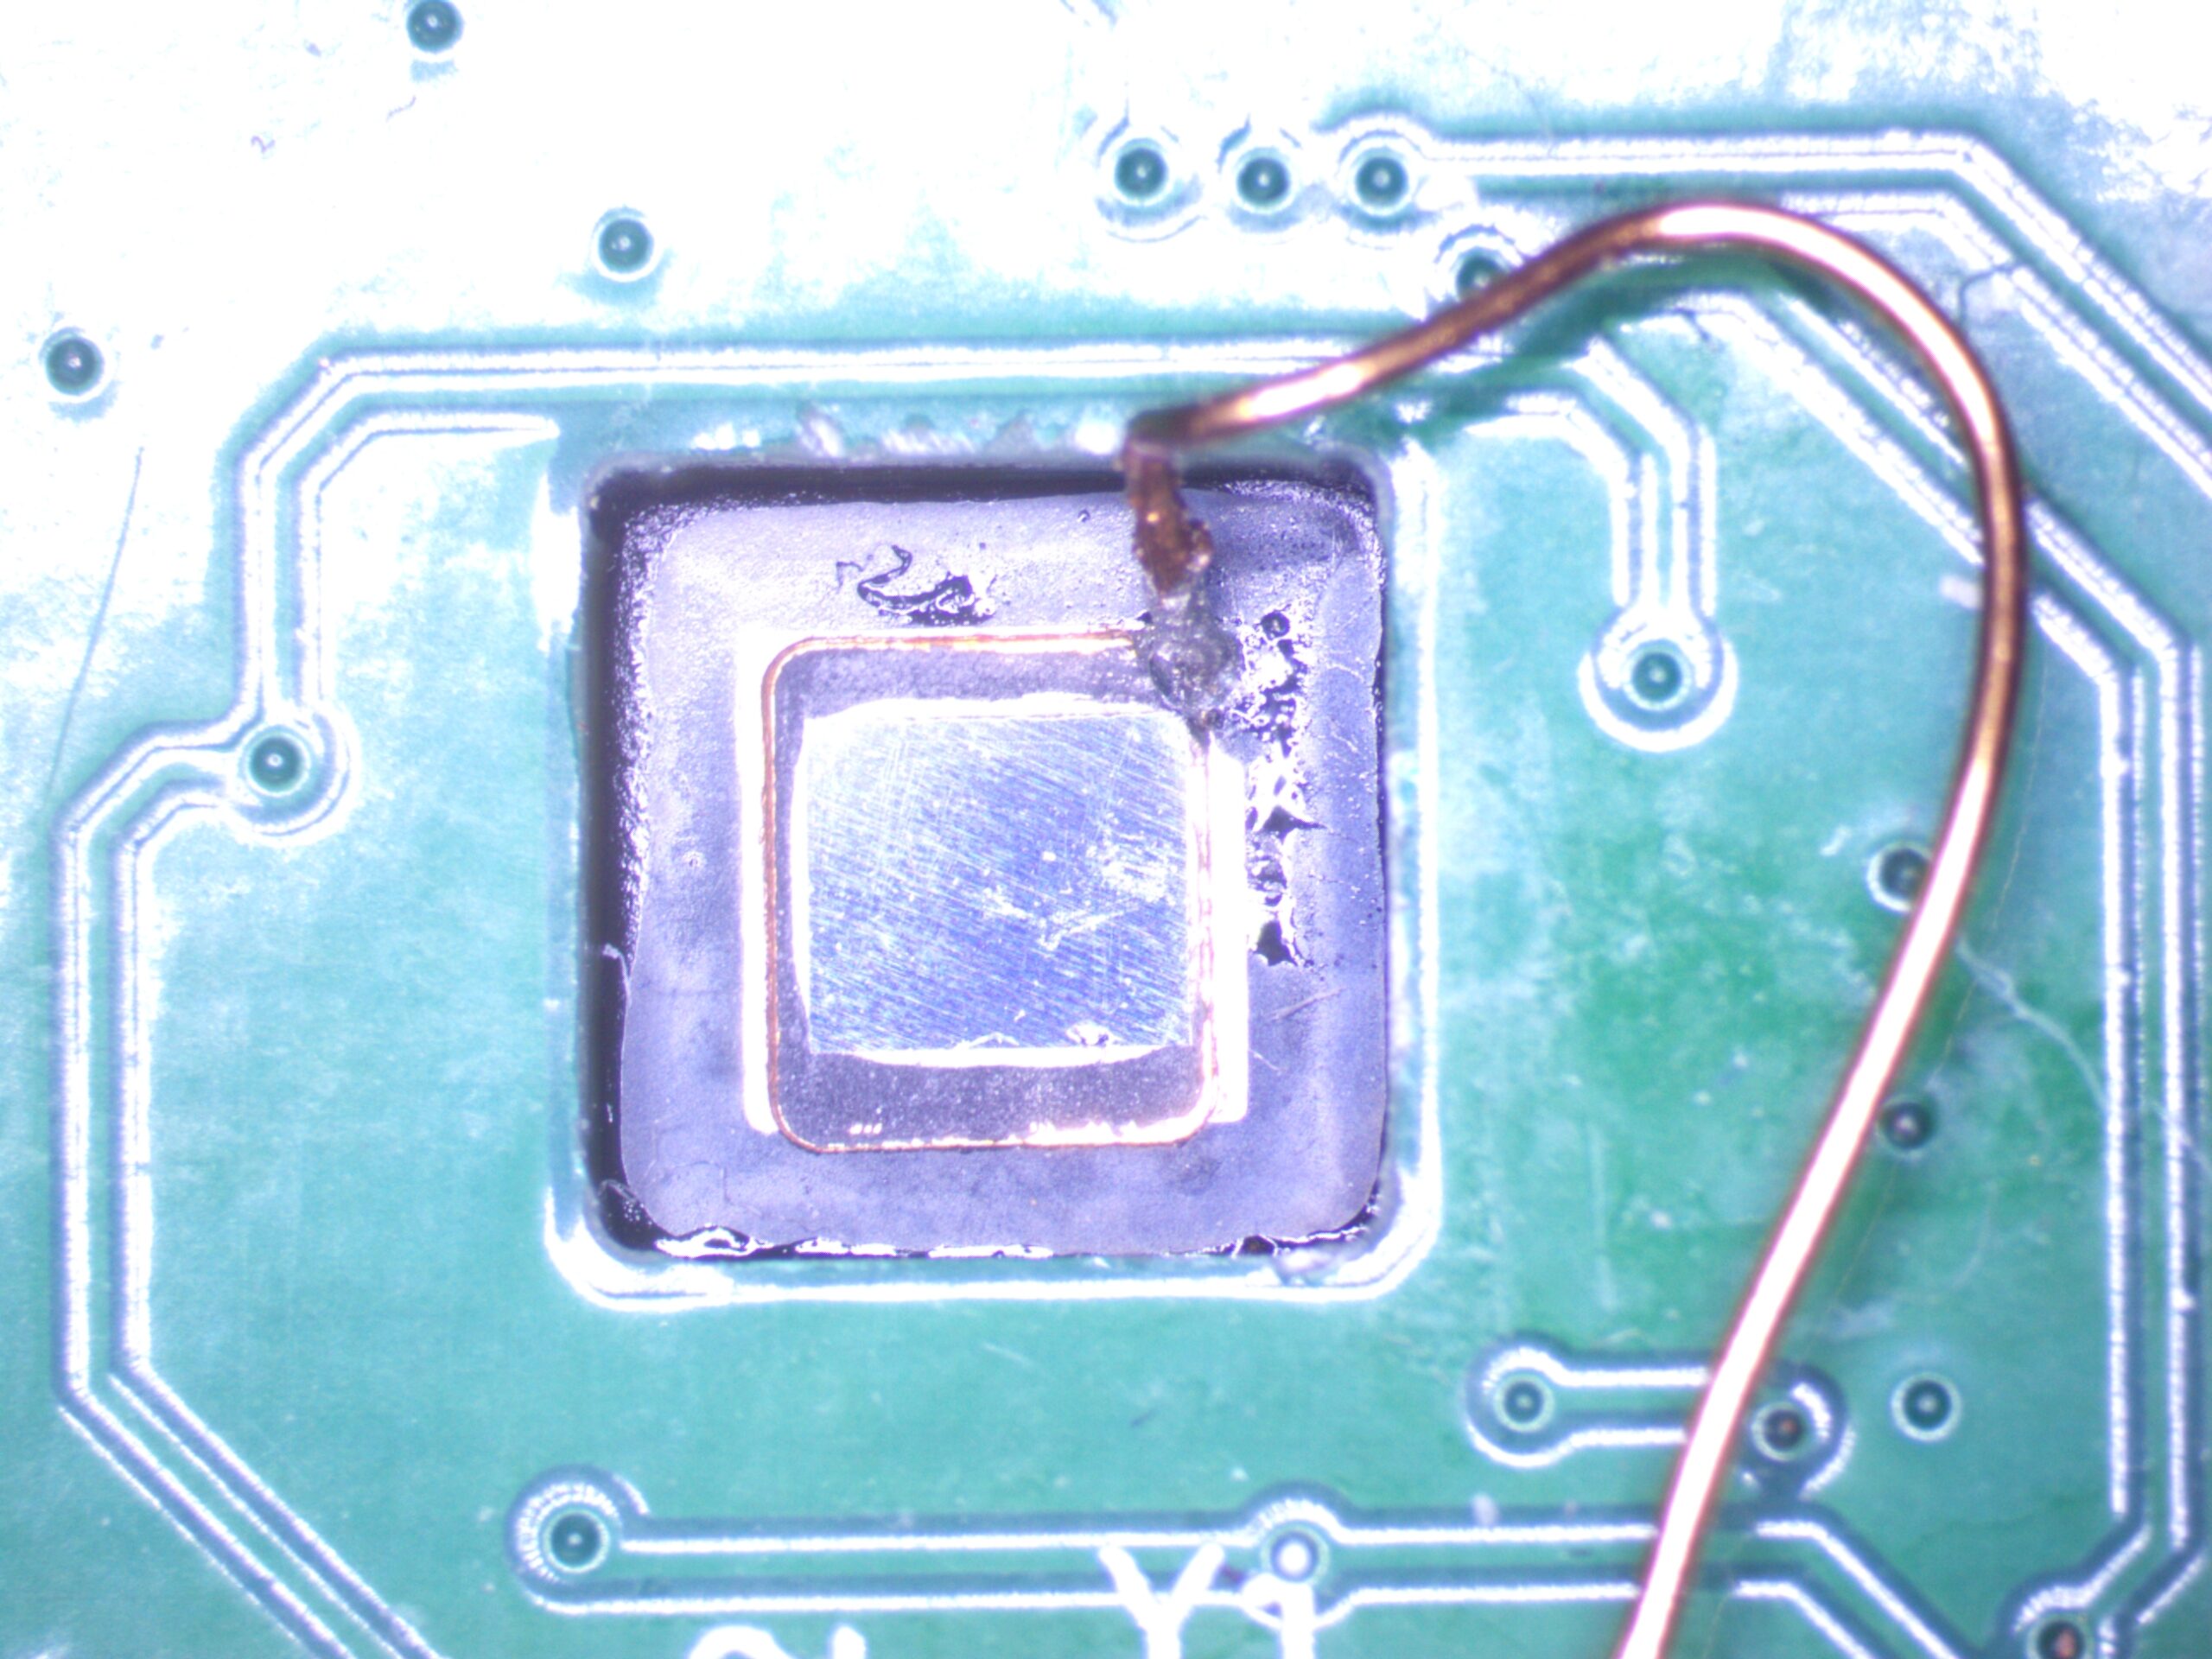
The RP2350 is actually a pretty secure chip, all things considered. It has secure boot, ARMv8 TrustZone to split secure and non-secure execution, and you can permanently disable debugging; the Pi Foundation even included fault detection, meaning the traditional “zap the chip until it obeys” technique is blocked. That’s why he [Ledger Donjon] The security team went full Bond Villain and tied everyone’s favorite fruity microcontroller to a table with a slowly approaching laser beam. The bench setup to do all this is quite impressive and comes with an impressive price tag of $250,000. Okay, movie clichés aside, the laser was very carefully focused on the target before turning it on. That target was the register that enables the 2350’s debugging functions. This register was located by uncapsulating the chip and examining the die with photon emission electron microscopy; The actual attack was carried out on a chip that had the cover removed on the back, with IR rays shining through the silicon wafer. There was probably more than a little trial and error to figure out exactly where on the die adjacent to the register to hit the laser to flip those bits. But they did it, restoring the debugger’s access to the safe execution zone. Then after resetting the chip, [Ledger]The team read the 128-bit secret that the Pi Foundation hid in memory as part of the 2350 hacking challenge. It has long been accepted that once black hats (or white hats, for that matter) get their hands on your hardware, they will find a way in. The effort it takes to get into a simple microcontroller here is really impressive. We’ve talked about laser fault injection before; Ironically, we’ve also featured Pi Pico-powered fault attacks, the kind that thwart this chip’s fault detection.